CBOM: the inventory that makes PQC real. See it to secure it.
Quantum risk isn’t solved by new algorithms alone; solving it starts with visibility.
That’s why your first step isn’t “new crypto”, it’s the inventory called a CBOM.
If you can’t see where RSA and ECC still protect revenue, software updates and confidential data, you can’t migrate them.
What’s a CBOM?
A Cryptographic Bill of Materials (CBOM) is a structured, machine-readable inventory that describes the cryptographic assets used by a system or application (algorithms, parameters, keys, certificates, trust stores, crypto libraries, protocols and signing workflows), together with how and where they are used.
You can think of it as an extension of the Software Bill of Materials (SBOM), but focused on the “crypto” under the hood.
Its primary purpose in the PQC era is to provide the visibility and agility needed to find and replace algorithms vulnerable to future quantum computers (such as RSA and ECC) with quantum-resistant standards (such as NIST’s ML-KEM and ML-DSA).
What Does a Comprehensive CBOM Include?
A robust CBOM goes beyond just listing libraries. Rather, it captures the granular details that enable true cryptographic risk management:
► Cryptographic Algorithms:
□ Type: RSA, ECDSA/ECDH, AES, SHA-256, ML-KEM, ML-DSA, etc.
□ Key Lengths/Parameters: such as RSA-2048, ECDSA P-384, ML-KEM-768.
► Cryptographic Libraries/Modules:
□ Name & Version: OpenSSL, BoringSSL, Windows CNG, Java JCE, etc.
□ Dependencies: mapping crypto assets to the specific software components that use them.
► Key & Certificate Material:
□ Certificates: X.509 certificates, issuance/expiry dates, issuer, signature algorithm.
□ Keys: key types (public/private/symmetric), storage (HSM, KMS, software keystore).
► Protocols & Usage:
□ Protocols: TLS version, SSH, IPsec, etc.
□ Cipher Suites: the specific combination of algorithms used for key exchange, encryption and hashing in a protocol session.
Best Practices & Industry Standards
The PQC transition makes crypto-agility a mandatory capability.
► Standardisation: Use an open format such as OWASP CycloneDX, which added CBOM to its core specification in version 1.6 (9 April 2024). The current version, CycloneDX 1.7 (21 October 2025), adds a standard registry of algorithm families and elliptic curves so tools name crypto consistently, and is published as the Ecma standard ECMA-424, 2nd edition (December 2025). A common format is key for automated tooling and cross-tool reporting.
► NIST Guidance: Align your migration plan with the NIST PQC standards (FIPS 203, 204 and 205, August 2024) and with NIST’s final transition plan, NIST IR 8547 (October 2026). It tells organisations to begin with cryptographic inventories, and it deprecates quantum-vulnerable public-key algorithms after 2030 and disallows them after 2035.
► Regulatory expectations: US federal agencies have had to submit a prioritised inventory of quantum-vulnerable cryptographic systems every year since May 2023 under OMB Memorandum M-23-02 (18 November 2022), and OMB M-26-15 (24 June 2026) now drives their migration plans. In the UK, the NCSC’s 2028 milestone expects organisations to have completed discovery of their cryptographic estate.
► Hybrid Schemes: Adopt a hybrid cryptographic approach during the transition. A good CBOM is essential for managing these dual implementations.
► Continuous Monitoring: Crucially, a CBOM should not be a one-time project. Refresh it as systems, certificates and suppliers change, so it stays a reliable basis for migration decisions.
Building the Inventory in Practice
A workable sequence for most organisations:
- Scope: start with your highest-value services and any system protecting data that must stay confidential for years.
- Discover: combine network scanning (TLS, SSH, IPsec endpoints), certificate and PKI sources, HSM and key management systems, and source-code and binary analysis. No single method sees everything.
- Record: capture findings in a standard format (CycloneDX CBOM), linked to system owners and business services.
- Assess and prioritise: rank quantum-vulnerable assets by data lifetime, exposure and ease of change.
- Plan and monitor: feed the inventory into your migration plan and keep it refreshed.
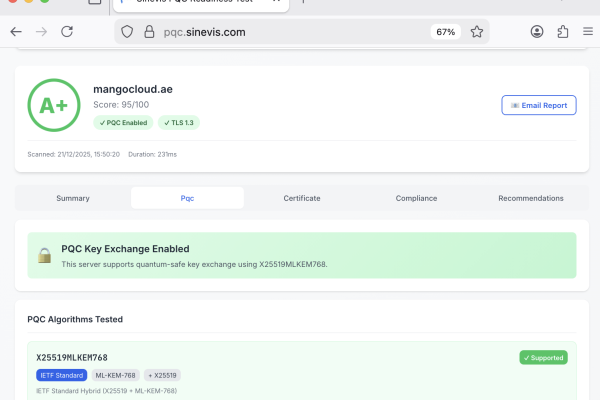
Tooling helps at scale. For example, Quantum Sentinel is an Enterprise Cryptographic Exposure Management platform for PQC discovery, cryptographic inventory (CBOM), exposure assessment and migration planning, using read-only metadata collection. To check a public website’s readiness today, try our PQC Compliance Check, or talk to us about post-quantum cyber readiness.
Final Thought: Prepare, Don’t Panic
Quantum computing doesn’t spell the end of cybersecurity, but it does require proactive adaptation.
The organisations that start preparing now will not only safeguard their data, but also gain a competitive advantage by demonstrating compliance and earning customer trust in the post-quantum era.
The future of cryptography is already being written.
The only question left is: will you be ready?
Our Post-Quantum Readiness Series
This article is Part 4 of our Post-Quantum Cyber Readiness Series, where we break down complex concepts into practical steps.
In this series, we covered:
- Part 1: Introduction to Post-Quantum Cryptography
Part 2: Understanding Quantum Threats and “Harvest Now, Decrypt Later” Attacks
Each article will equip CEOs, CISOs, IT leaders and architects with the knowledge and tools to navigate the quantum transition confidently.