When to Consider a SOC 2 Report
SOC 2 is an AICPA attestation report, not a certification. When to get one, Type I vs Type II, and the five Trust Services Criteria categories explained.
When to Consider a SOC 2 Report Read More »
Best practices and Knowledge base on Governance Risk Compliance
SOC 2 is an AICPA attestation report, not a certification. When to get one, Type I vs Type II, and the five Trust Services Criteria categories explained.
When to Consider a SOC 2 Report Read More »
Why fintech companies are replacing passwords with passkeys and FIDO2: phishing resistance, faster sign-ins, PSD2 SCA, PCI DSS v4.0.1 and NIST SP 800-63-4.
Going Passwordless: Why Fintech Companies Are Moving to Passkeys Read More »
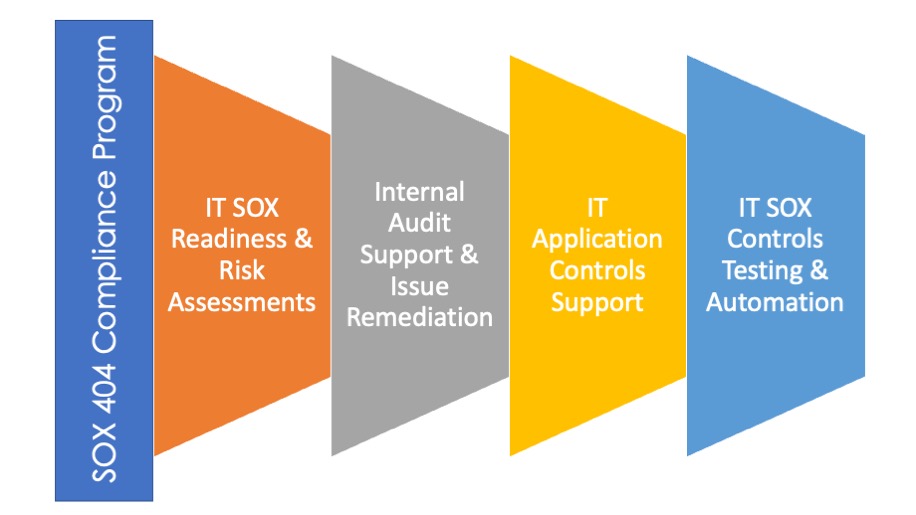
What the Sarbanes-Oxley Act (SOX) requires: Sections 302, 404, 409, 802 and 906, SOX controls, IT general controls, the annual audit and a practical checklist.
Sarbanes-Oxley (SOX) Compliance Read More »
How IT governance, as part of corporate governance, makes IT investment deliver business value, and how COBIT 2019 (with COBIT 7 announced) and ITIL support it.
Role of IT governance on value delivery Read More »
Three common challenges in IT risk management: who makes risk decisions, superficial risk assessments and a closed culture, mapped to NIST CSF 2.0 and ISO/IEC 27001:2022.
Common Challenges in IT Risk Management Read More »